What SGP.32 Means for Enterprise IoT at Scale
SGP.32 can simplify profile changes, lower fieldwork, and improve IoT flexibility at scale.
SGP.32 can simplify profile changes, lower fieldwork, and improve IoT flexibility at scale.
Filter articles
Where permanent roaming rules break IoT deployments, why regulators impose them, and what to use instead of a roaming SIM in restricted markets.
What NIS2 asks of IoT and OT connectivity in EV charging networks, which Article 21(2) technical controls apply, and what stays your responsibility.
The five layers of a modern IoT connectivity architecture, from SIM identity to Zero Trust enforcement, and where cross-border deployments break.
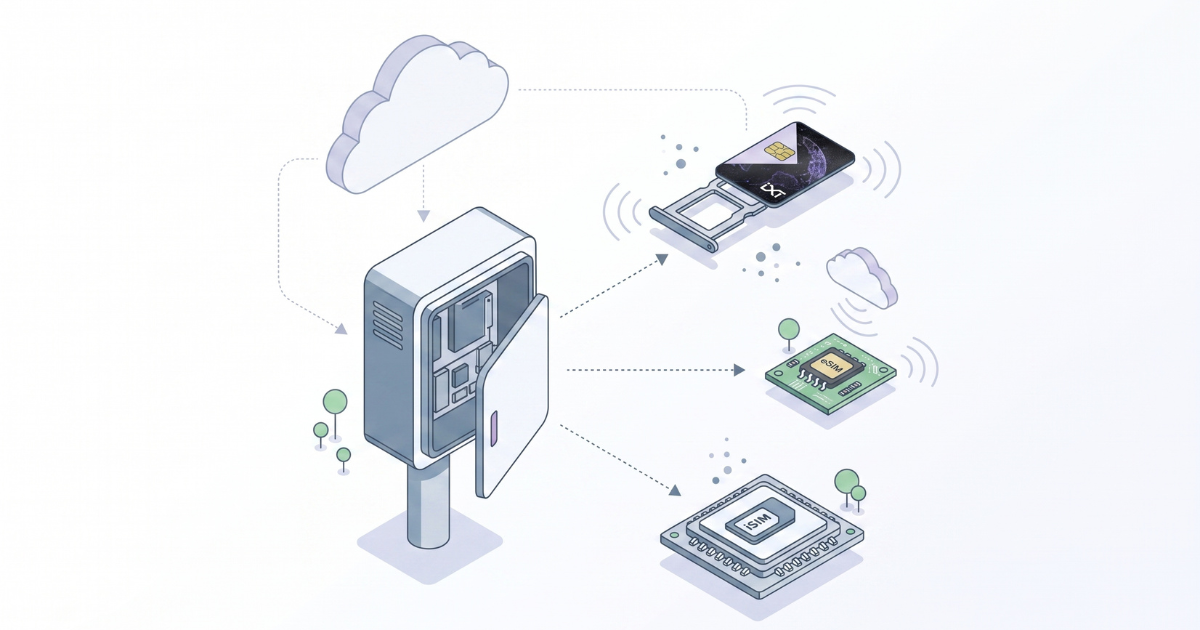
IoT SIM, eSIM or iSIM for a multi-country deployment? The form factor sets provisioning and board space. The provider decides everything that comes after.
A private APN keeps industrial IoT traffic off the public internet. It does not show what your devices talk to. Here is what closes that gap.
Zero Trust for headless IoT devices moves enforcement off the device into the network, so sensors that run no software still get identity-based access.
Secure IoT connectivity protects distributed industrial devices at the network layer. Learn what it means, why VPNs fail at fleet scale, and what works instead.
A global IoT SIM connects devices across countries and mobile networks on one contract. Here is how IoT SIM cards authenticate, roam, and stay under control.