Securing your IoT devices: 8 lessons from IXT and Illumio
Eight lessons from IXT and Illumio on securing IoT and OT devices that cannot run agents: patch limits, Zero Trust, visibility and lateral movement.
Eight lessons from IXT and Illumio on securing IoT and OT devices that cannot run agents: patch limits, Zero Trust, visibility and lateral movement.
Filter articles
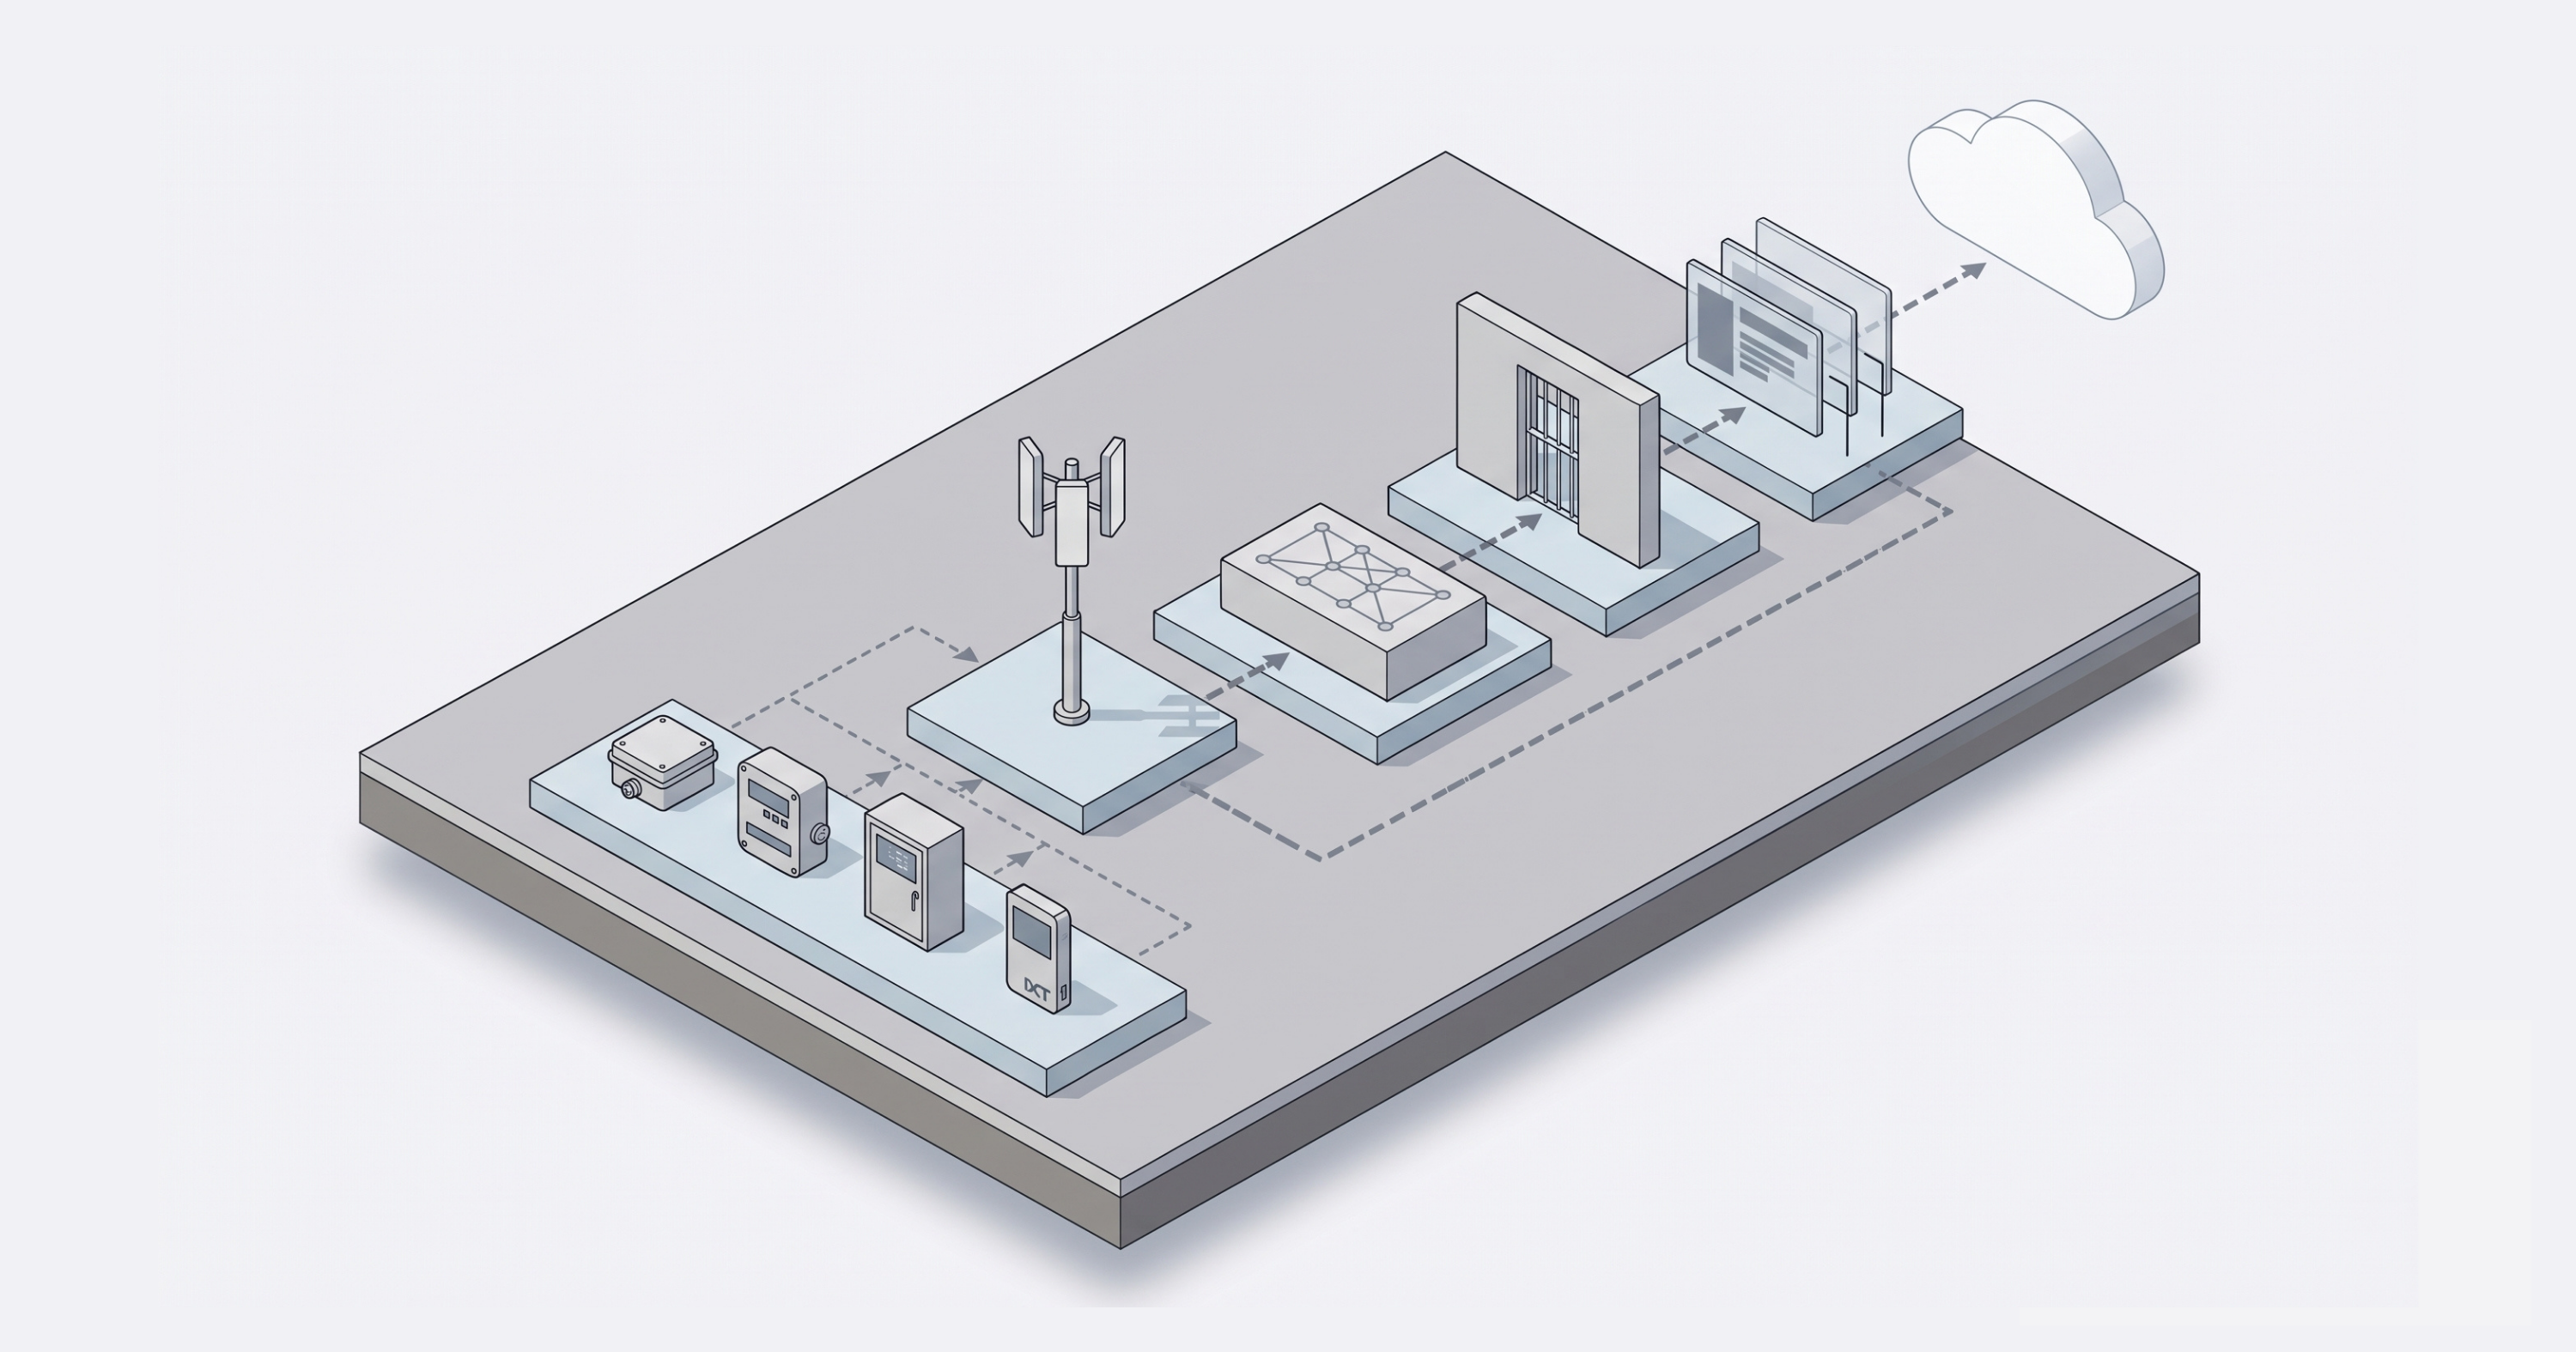
How IoT data moves from device and radio access through transport, security, management, and cloud, and which control points decide reliability and risk.
OT devices cannot run agents and cannot be patched on an IT cadence. Where OT security differs from IT, and what to enforce at the network layer instead.
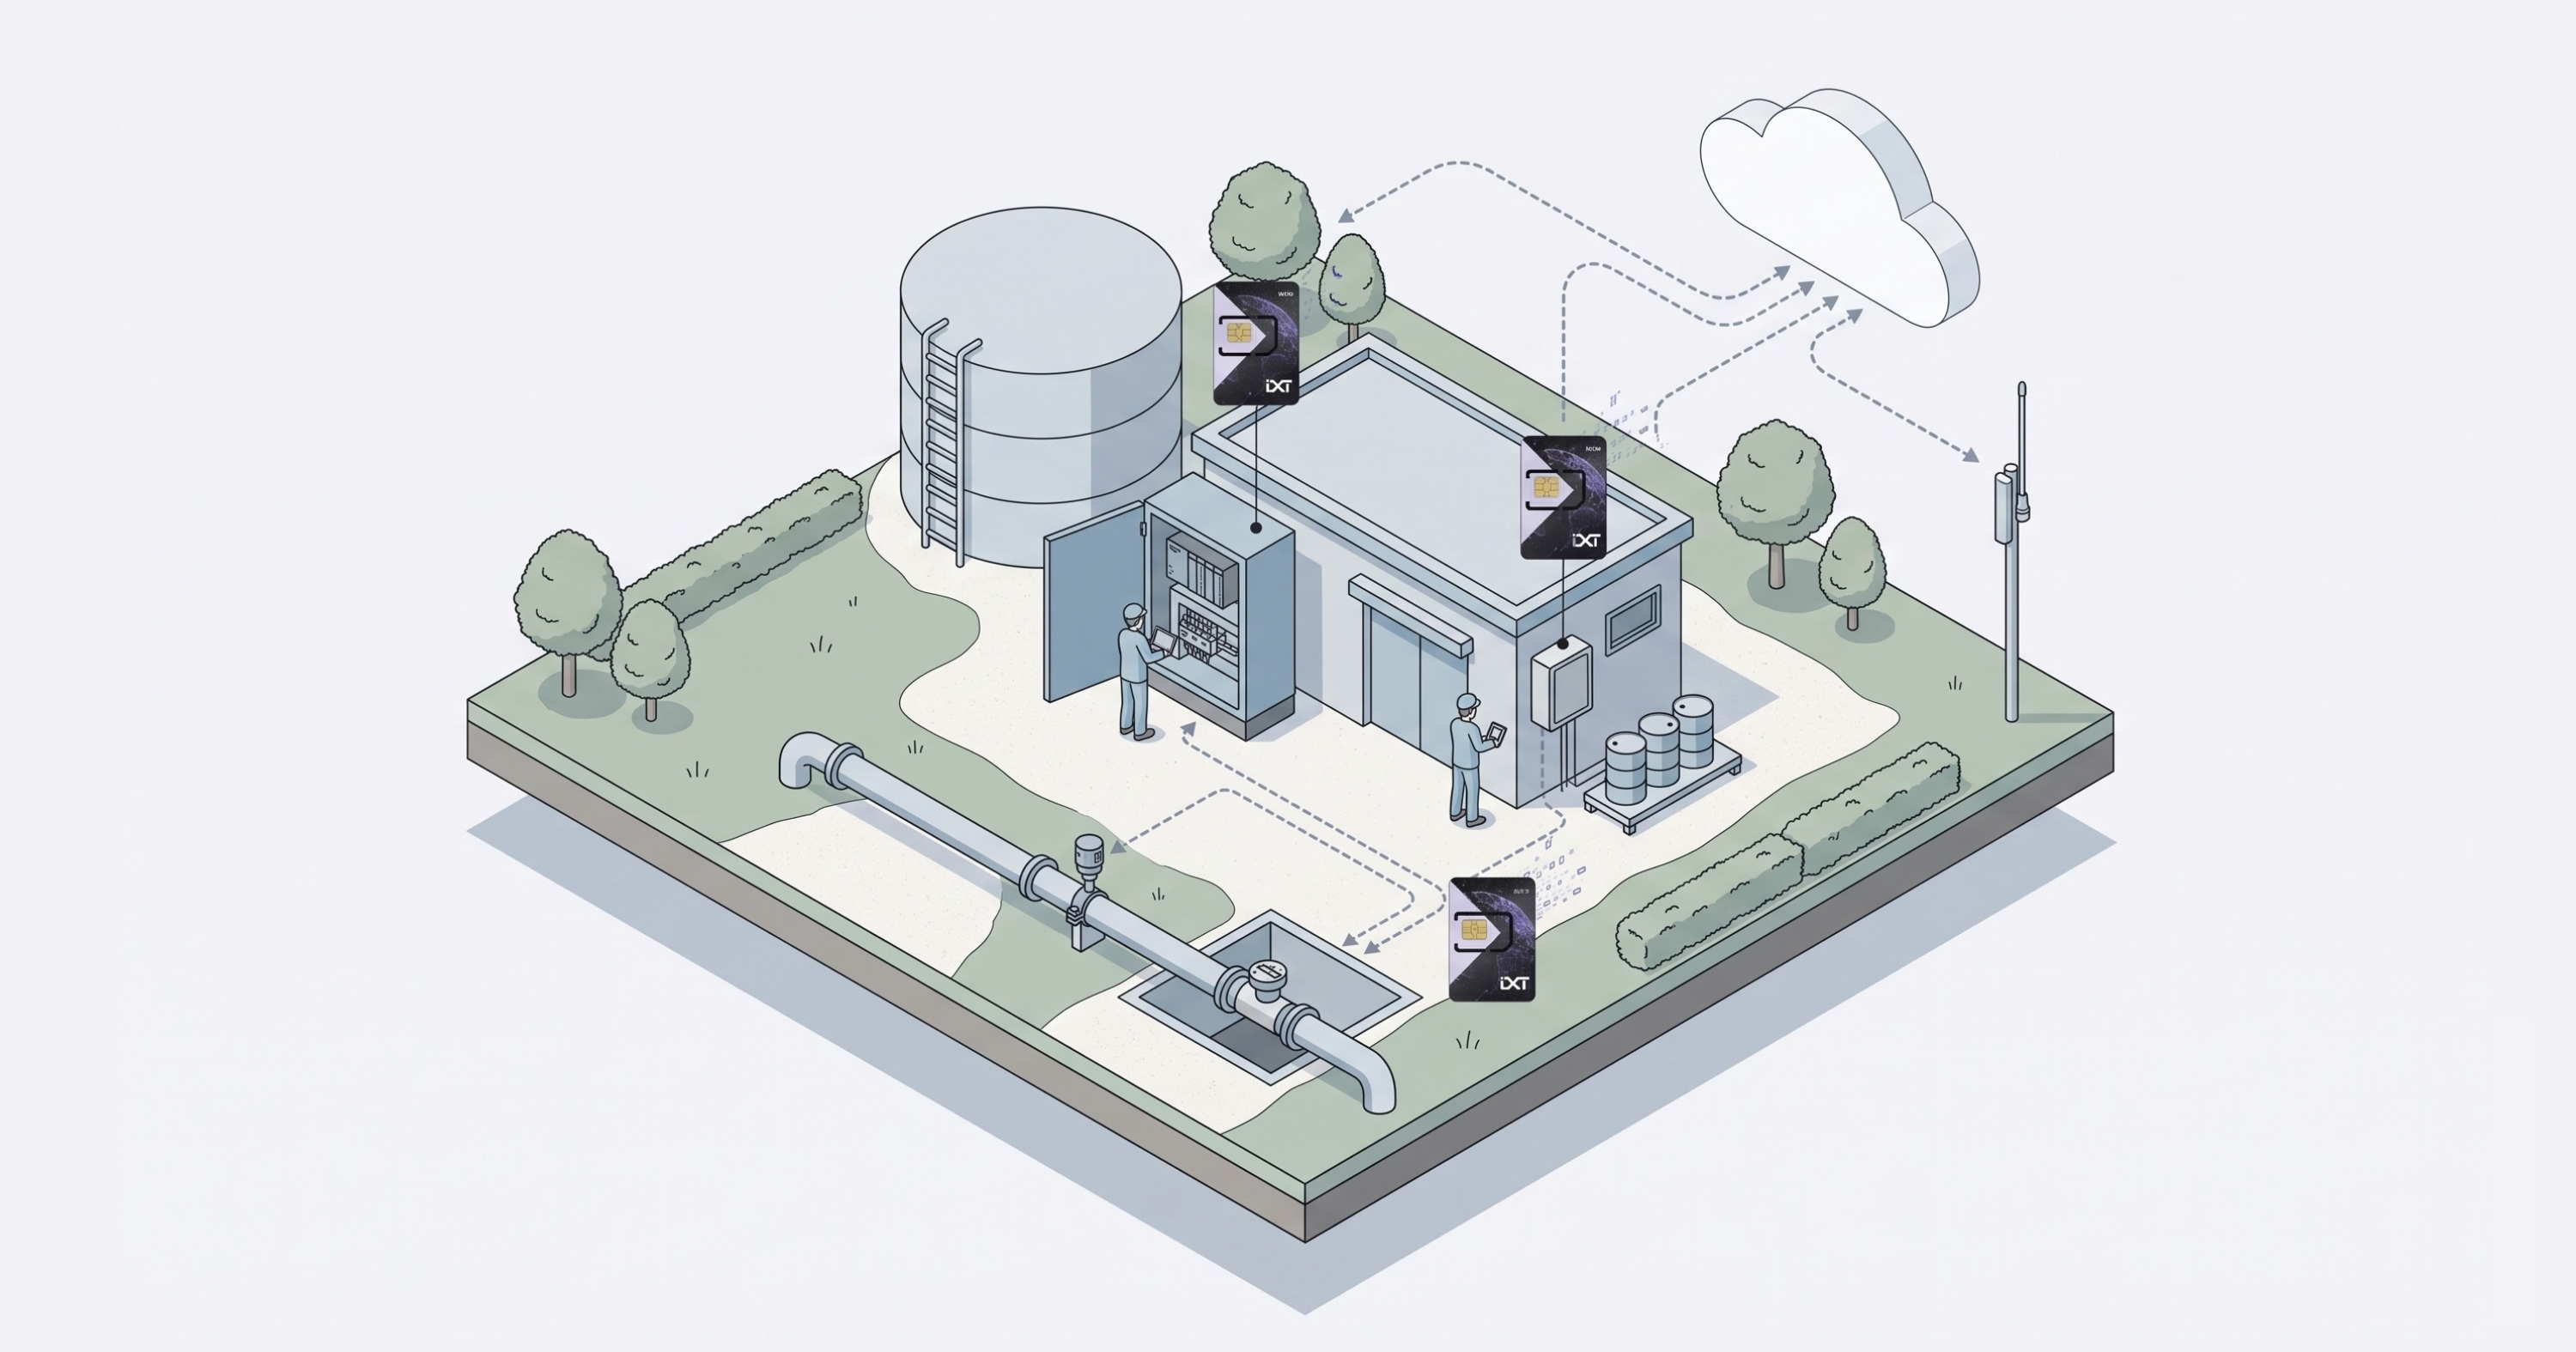
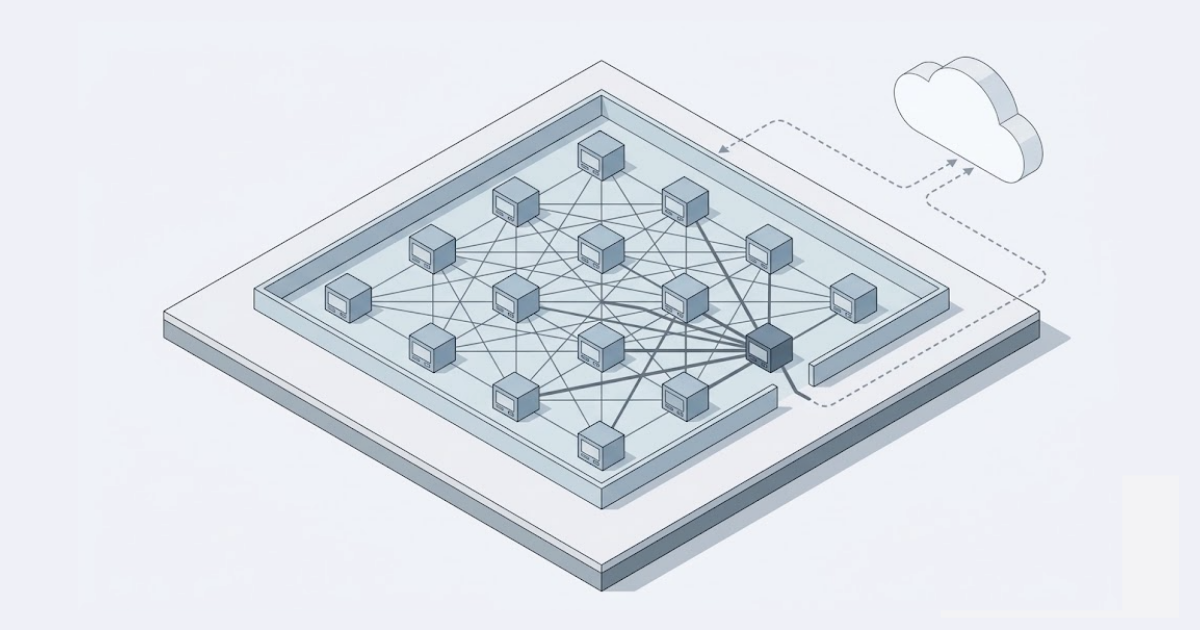
A private APN keeps IoT traffic off the public internet. It does not stop a compromised device reaching the rest of your fleet. Here is what the APN layer leaves undefended, and what closes the gap.
Zero Trust assumes an agent on every endpoint. Headless IoT devices run none. Here is how identity, least privilege, and audit move into the network instead.
NIS2 names outcomes, not network designs. What Article 21(2) asks of EV charging OT connectivity, and which parts of it remain the operator's own work.
The four IoT architecture layers explain how data moves, not how it is protected. Here is what the security layer does, and where it belongs.
Smart meters cannot run a VPN client, so the tunnel ends upstream and the estate goes flat. What replaces legacy VPNs for utility grid devices in 2026.
Enterprise IoT SIM pricing looks clean until the invoice lands. Where the hidden fees come from, and what predictable per device pricing actually requires.